Authentication should verify not only who you are, but also whether you are connecting to the real hospital website.
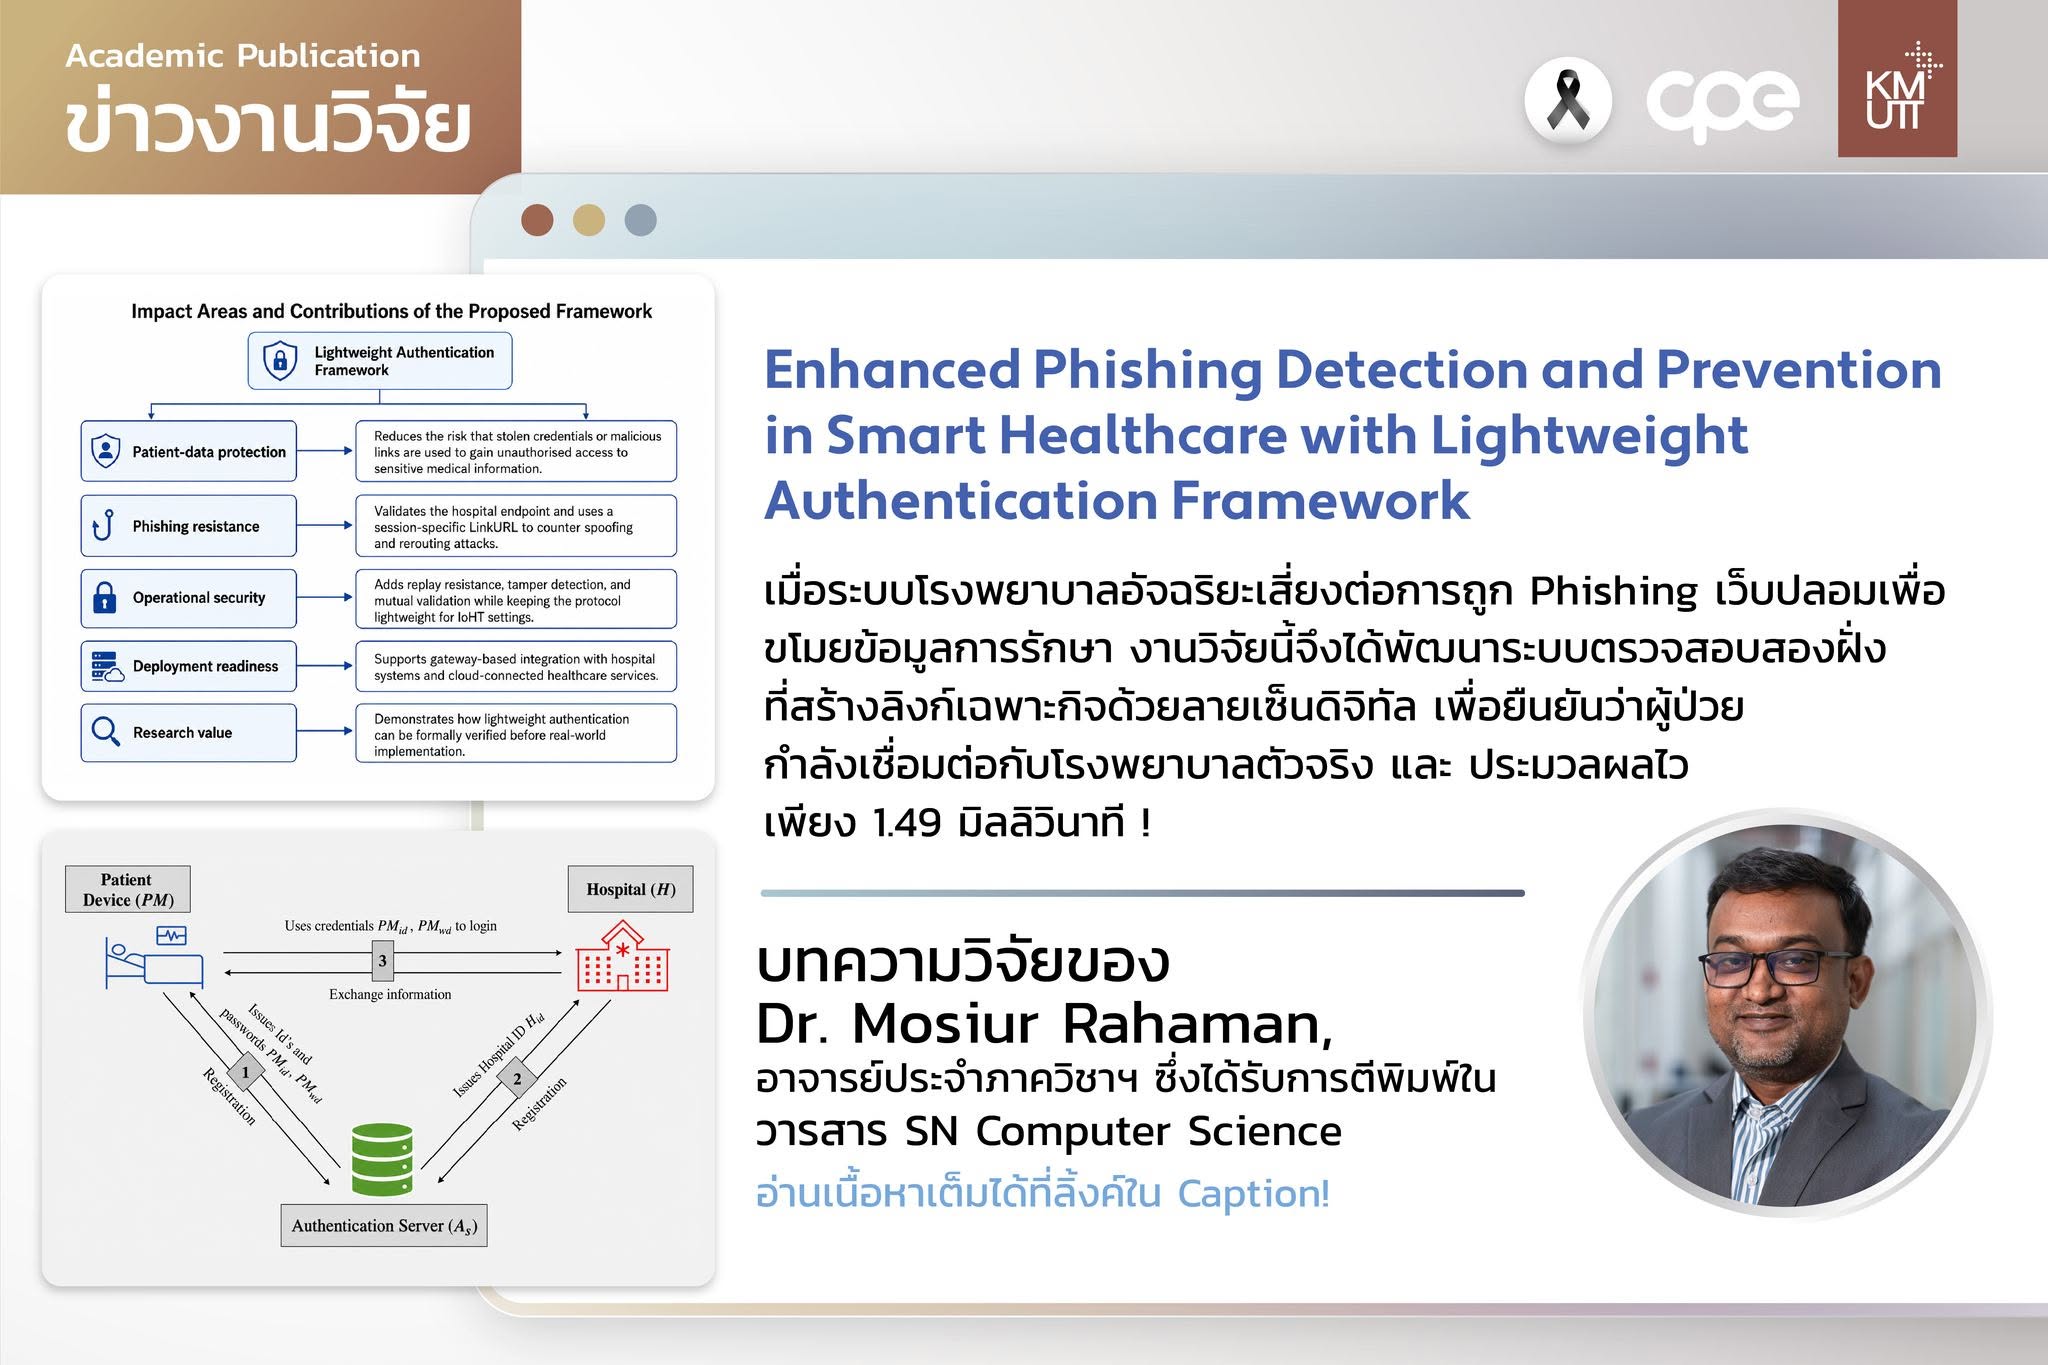
In smart healthcare systems, where medical devices and digital services are interconnected, fake websites can expose patient records and hospital infrastructure to cyberattacks. Research from the Computer Engineering Department at King Mongkut’s University of Technology Thonburi (CPE KMUTT) introduces an authentication approach that verifies both the user and the destination before establishing a connection.
The system uses a trusted intermediary server to validate both parties and generate a one-time link for each connection. This is combined with a temporary code, a personal PIN, and a digital signature bound to the connection context to help prevent users from connecting to fraudulent hospital websites.
Testing showed a processing time of just 1.49 milliseconds, indicating potential for use with resource-constrained medical devices. The research also presents a formal mathematical security proof under a defined threat model.
The study was published in SN Computer Science.
Read the full paper: https://kmutt.me/HG4qGi1